I. Patent Overview
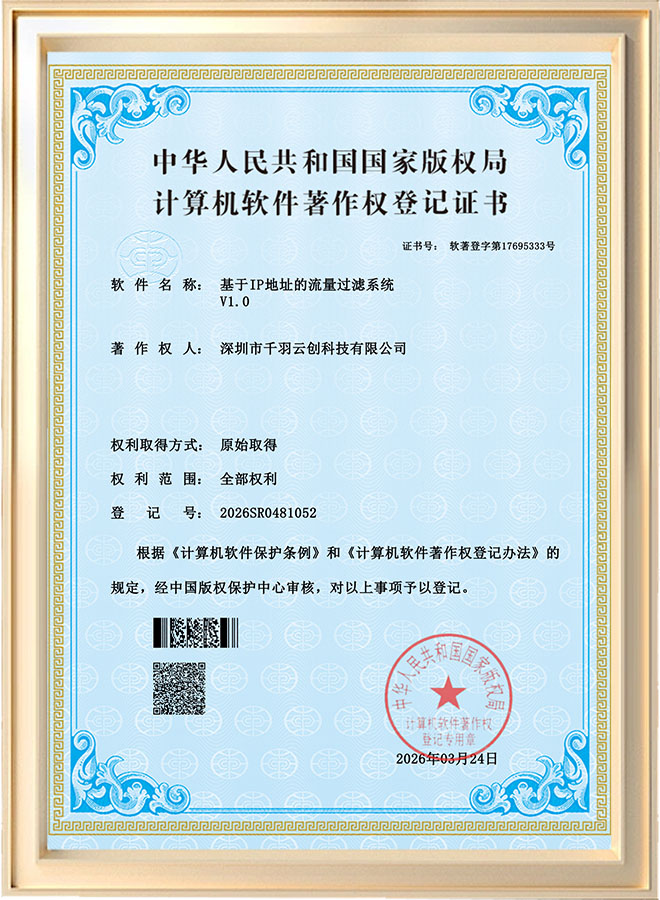
This patent involves an efficient network access control technology that achieves refined traffic filtering and management by deeply parsing source IP addresses and destination IP addresses within data packets, combined with a preset access policy library.
Compared to traditional IP filtering solutions, this patent achieves innovations in the following areas:
●Intelligent Policy Matching: Supports flexible rule configuration based on multiple dimensions such as IP ranges, IP subnets, and geographic locations, meeting access control requirements in complex scenarios
●High-Performance Processing Architecture: Optimized matching algorithms significantly reduce CPU resource consumption for filtering operations, maintaining wire-speed forwarding even under high-concurrency traffic
●Dynamic Policy Updates: Supports online hot updates of policy libraries, allowing new filtering rules to take effect without device restarts or service interruption
●Detailed Logging: Completely records information on both blocked and allowed traffic, providing data support for security auditing and troubleshooting
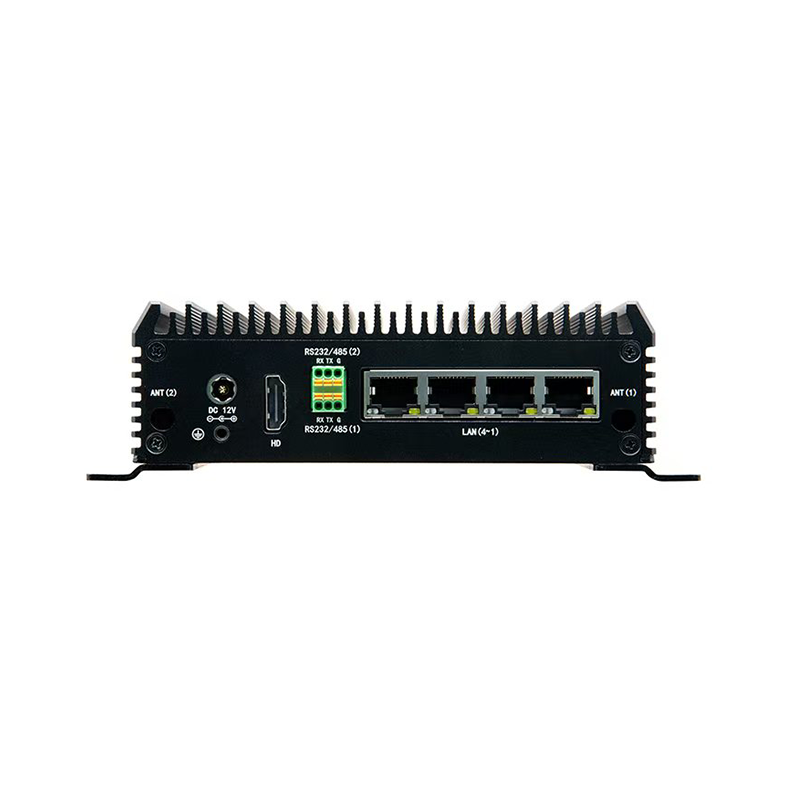
This patented technology has been deeply integrated into the company‘s core product lines, providing a solid technical foundation for network security and access control in industrial scenarios.
II. Application Value of the Patented Technology Across Different Products
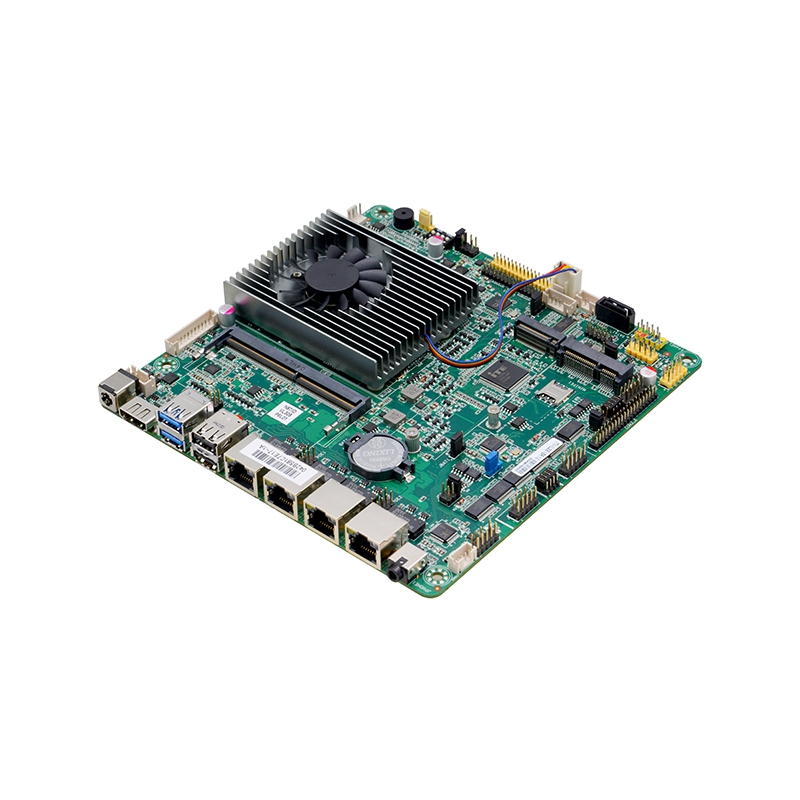
1. Industrial Motherboards
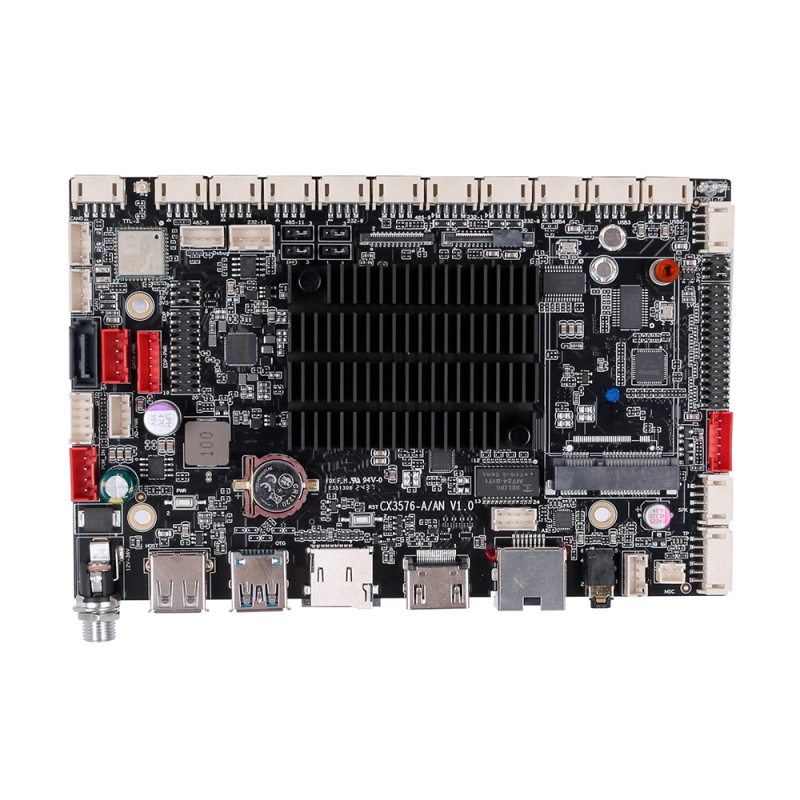
As the underlying computing platform for industrial devices, industrial motherboards integrated with this patented technology possess native-level network access control capabilities while providing foundational computing power.
●System-Level Security Protection: Enables IP filtering at the firmware layer before the operating system boots, effectively defending against underlying network attacks
●Reduced Host CPU Burden: Offloads traffic filtering tasks to the motherboard hardware level, freeing CPU resources for core business processing
●Customized Access Control: Supports customized whitelist/blacklist policies based on application scenarios, allowing only authorized devices or host computers to access the industrial motherboard, preventing unauthorized access
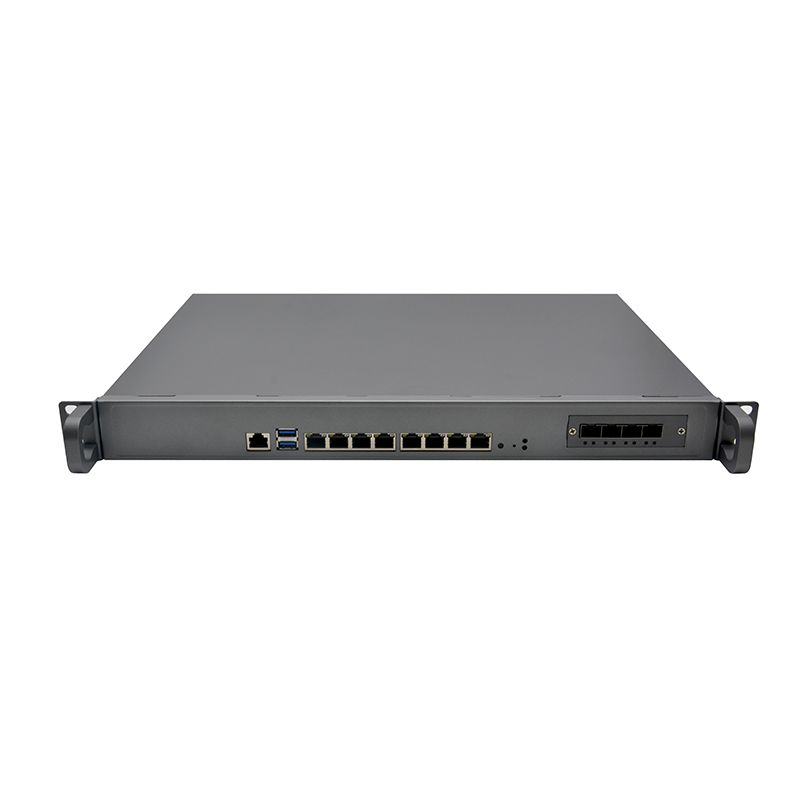
2. Firewalls
Firewalls serve as the boundary guardians of network security. This patented technology provides core access control capabilities for firewall products.
●Granular Access Control: Refined IP address-based filtering enables differentiated access permission management for different departments and business systems
●Intrusion Prevention Coordination: Integrates with intrusion detection modules to automatically add attack source IPs to blacklists, enabling dynamic threat blocking
●Network Zone Isolation: Supports establishing IP-based access control policies between different network zones (such as production networks, office networks, and management networks), effectively preventing lateral threat propagation
●Compliance Support: Meets functional requirements for access control stipulated by regulations such as China‘s Classified Cybersecurity Protection (MLPS) 2.0 and industrial control system security protection requirements
3. Industrial Monitors
Industrial monitors are typically deployed as human-machine interface (HMI) units. This patented technology endows them with network-level security protection capabilities.
●Restricts Unauthorized Access: Through IP filtering mechanisms, only controllers, PLCs, or host computers from specific subnets or specific IP addresses are allowed to communicate with the monitor, preventing malicious device access
●Ensures Display Content Security: Prevents unauthorized sources from tampering with display content or injecting malicious commands, ensuring the integrity and authenticity of the operation interface
●Simplifies On-Site Security Management: In distributed deployment scenarios (such as multiple production lines), uses IP filtering to restrict each monitor to communicate only with control equipment on its own line, avoiding cross-line operational errors
4. Industrial Panel PCs
Industrial panel PCs integrate display, computing, and communication functions and are widely used in edge computing and on-site control scenarios. This patented technology builds a multi-layered access control system for them.
●Edge Node Security Hardening: As edge computing nodes, uses IP filtering to restrict data reading and remote operations and maintenance to cloud platforms or authorized host computers only, preventing unauthorized access
●Multi-Service Isolation: When a panel PC runs multiple business applications simultaneously, communication ranges for different applications can be restricted based on IP addresses, achieving logical isolation between services
●Mobile Scenario Protection: In mobile application scenarios such as AGVs or in-vehicle systems, IP filtering mechanisms ensure that the panel PC communicates only with specific servers, preventing unauthorized scanning and attacks in public network environments
●Data Security Protection: Restricts access requests from unauthorized devices, effectively preventing sensitive production data from being illegally stolen or tampered with
III. Core Value Summary
Regardless of which product category you choose from our company, this patented technology delivers the following core values:
Security Compliance: Meets regulatory requirements for access control such as MLPS 2.0 and industrial security protection standards
Perimeter Protection: Effectively prevents unauthorized device access, blocking illegal access and data breaches
Service Isolation: Achieves access isolation between different business systems and different network zones
Performance Optimization: Hardware-level filtering reduces CPU burden, ensuring core business processing performance
Simplified Operations:Flexible policy configuration and dynamic updates reduce security management complexity
Note: This patent has been authorized by the National Intellectual Property Administration. The related technology has been applied across our full range of products. Please contact us for more information:[email protected]




 WhatsApp


 Teamas

